


SDLA Compliance Resource
Maintain a Useful District Technology Plan Without Inventing a State Deadline
A strategic governance cycle for instructional technology, infrastructure, cybersecurity, accessibility, privacy, staffing, lifecycle costs, and continuity—not a fictitious annual filing requirement.
In Plain Language: E-Rate no longer imposes a general technology-plan requirement. Maintain a plan because coordinated technology decisions require one, and separately calendar any plan or approval required by a specific funding source or local policy.
Why this matters
Treating the plan as nonexistent creates fragmented purchases and unowned risk; treating it as a universal annual compliance filing invents work. The right control is a living, locally governed roadmap tied to budgets and service levels.
Primary ownership
Primary owner: technology leader with superintendent/cabinet sponsor. Handoff partners: instruction, special education/accessibility, cybersecurity/privacy, business/procurement, facilities, HR, libraries, communications, and site leaders.
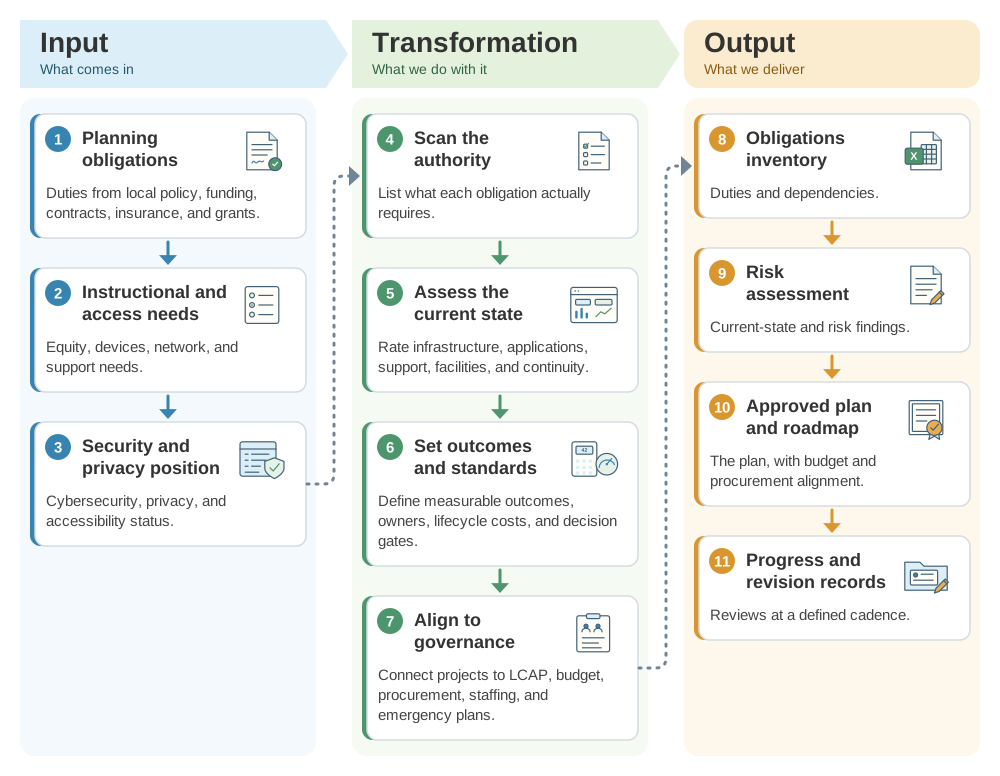
From local obligations to a useful district technology plan: the SDLA ITO workflow
No general state or E-Rate deadline applies, so the plan's value comes from coordinated decisions and from any funding-specific duty. This SDLA ITO (Input, Transformation, Output) graphic shows how the planning obligations, the current technology environment, and instructional needs become the obligations inventory, the approved plan and roadmap, and the progress records.
Operational workflow
- Inventory the actual planning obligations attached to local policy, funding, contracts, insurance, and grants.
- Assess instructional needs, access/equity, devices, network, applications/data, interoperability, cybersecurity, privacy, accessibility, support capacity, facilities, and continuity.
- Set measurable service outcomes, standards, owners, lifecycle costs, dependencies, and decision gates.
- Align projects to LCAP, budget, procurement, staffing, records, and emergency planning.
- Review progress and risks at a locally defined cadence; revise after material changes.
Implementation pathway
Evidence to retain
- Authority/dependency inventory
- Current-state and risk assessment
- Approved plan/roadmap
- Budget/procurement alignment
- Progress and revision records
Official guidance and help
- FCC E-Rate Modernization OrderElimination of E-Rate technology-plan requirement
- FCC E-Rate OverviewCurrent program context
- CISA K–12 ResourcesCurrent cybersecurity planning support
Source review completed August 30, 2026. Verify current federal and California requirements, CDE/FCC guidance, local policy, public-meeting procedures, records, and final submitted or adopted state before acting.