


SDLA Compliance Resource
Complete Annual CAASPP Security Agreements Before Secure Access
A role-based annual attestation and training control for TOMS users and non-TOMS personnel who handle secure content or enter testing environments.
In Plain Language: TOMS users complete the applicable online security forms; non-TOMS staff with secure access complete the current non-TOMS affidavit. All covered staff receive local annual security training before work begins.
Why this matters
A prior-year signature does not carry forward. Missing forms or poorly defined coverage expose test content, student credentials, and PII and complicate incident response.
Primary ownership
Primary owner: LEA CAASPP coordinator. Partners: site coordinators, supervisors, test administrators/examiners, proctors, substitutes, technology, custodial/room staff as applicable, and privacy/security.
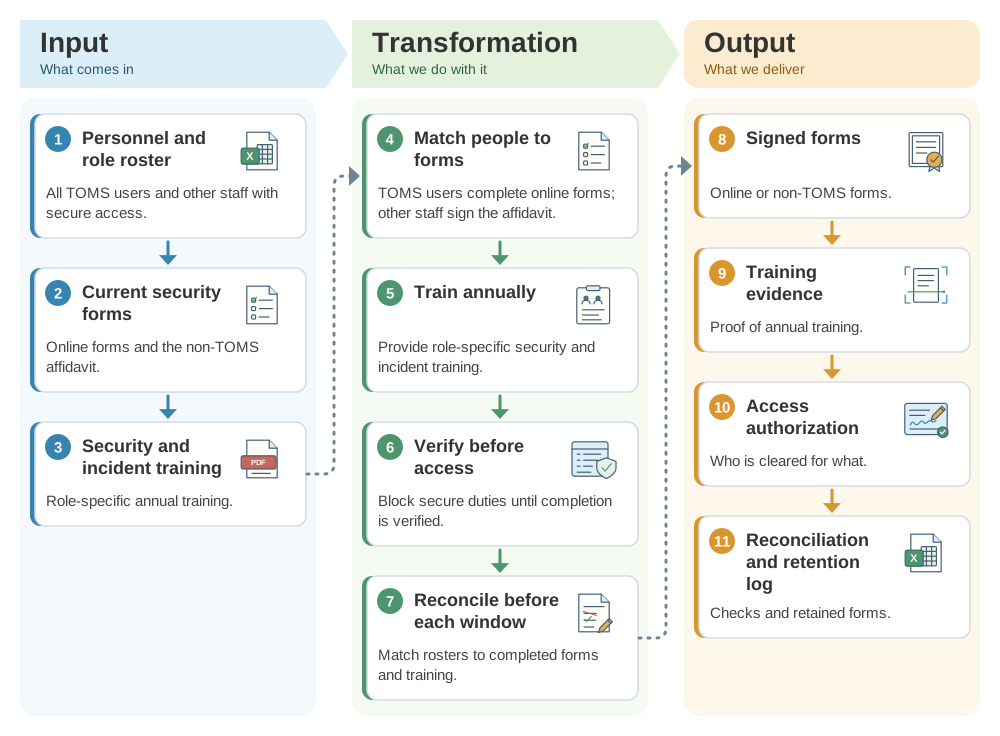
From a covered-person roster to cleared secure access: the SDLA ITO workflow
Secure duties are blocked until the right form and training are verified. This SDLA ITO (Input, Transformation, Output) graphic shows how every person who will touch TOMS, secure content, credentials, rooms, or materials become the roster, the signed forms, the training evidence, and the access authorization.
Operational workflow
- Inventory every person who will access TOMS, CERS, secure content, credentials, rooms, or materials.
- Map TOMS users to online forms and other covered staff to the current non-TOMS affidavit.
- Provide role-specific annual security and incident training.
- Block secure duties until completion is verified.
- Reconcile rosters before each window and retain forms under current rules.
Implementation pathway
Evidence to retain
- Personnel/role roster
- Signed online or non-TOMS forms
- Training evidence
- Access authorization
- Reconciliation and retention log
Official guidance and help
- Test SecurityCurrent forms, STAIRS, and security controls
- July 2026 CAASPP Communication2026–27 form and training reminder
- TOMS ResourcesCurrent account guidance
Source review completed August 30, 2026. Verify current California requirements, CAASPP and ELPAC manuals, live system status, local policy, pupil records, and final system state before acting.