


SDLA Compliance Resource
Assign 2026–27 TOMS Roles by Function and Site
A least-privilege provisioning process for coordinators, administrators, examiners, educators, and interim-assessment users.
In Plain Language: Match each person’s duties to the narrowest current role, correct LEA/site, and required training. Verify the account works before—not during—the testing session.
Why this matters
Role names that sound similar can expose different students, systems, or secure materials. Incorrect assignment creates privacy risk or prevents lawful administration.
Primary ownership
Primary owner: LEA coordinator; site coordinators manage authorized site-level users within current rules. Partners: supervisors, HR, privacy/security, technology, and training leads.
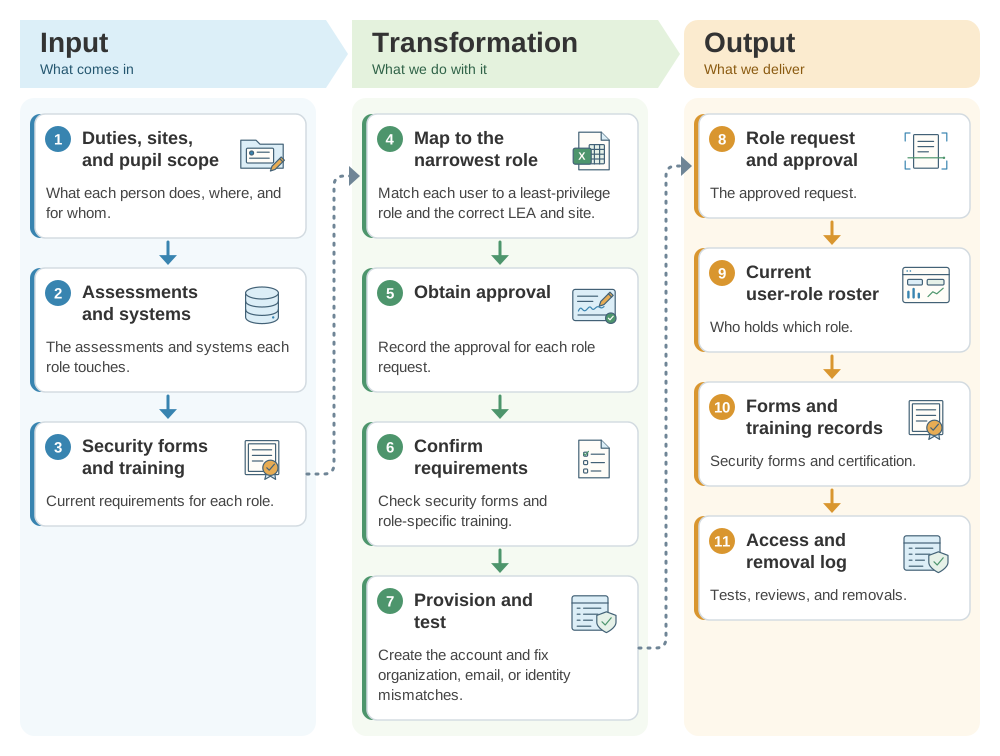
From job duties to tested, least-privilege TOMS roles: the SDLA ITO workflow
Each person gets the narrowest role that fits their duties, and the account works before testing begins. This SDLA ITO (Input, Transformation, Output) graphic shows how each user's duties, sites, and pupil scope, and the required forms and training become the approved role requests, the user-role roster, and the access and removal log.
Operational workflow
- Inventory duties, sites, pupil scope, assessments, and systems required.
- Map each user to the least-privilege role and obtain approval.
- Confirm security forms and role-specific training/certification.
- Provision and test access; correct organization, email, or identity mismatches.
- Review during the year and remove access immediately when duties end.
Implementation pathway
Evidence to retain
- Role request/approval
- Current user-role roster
- Security forms
- Training/certification
- Access and removal log
Official guidance and help
- TOMS ResourcesCurrent role and user guidance
- Test SecurityForms for TOMS and non-TOMS users
- CAASPP & ELPAC HomeCurrent systems and guides
Source review completed August 30, 2026. Verify current California requirements, CAASPP and ELPAC manuals, live system status, local policy, pupil records, and final system state before acting.