


SDLA Compliance Resource
Rebuild TOMS Access After the Annual Role Rollover
A year-boundary access review that replaces deactivated prior-year roles with approved 2026–27 assignments.
In Plain Language: On July 7, current-year roles become available and prior-year roles deactivate. Reauthorize only personnel with a current job need, correct organization/site, completed requirements, and named approver.
Why this matters
Blindly copying last year preserves excessive access; waiting until testing creates emergencies. TOMS roles also govern access to student PII, CERS, secure content, and other systems.
Primary ownership
Primary owner: LEA CAASPP/ELPAC coordinators. Partners: HR, site coordinators, technology/identity management, privacy/security, supervisors, and program owners.
From prior-year roles to reauthorized TOMS access: the SDLA ITO workflow
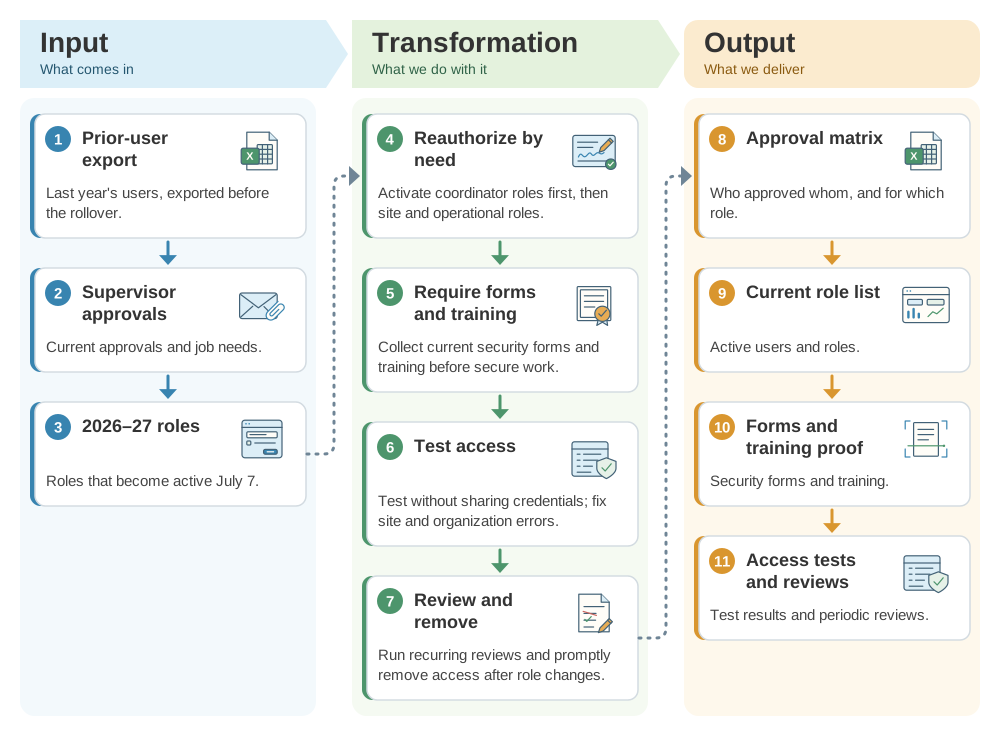
After the July 7 rollover, each person's access should reflect a current job need and a named approver. This SDLA ITO (Input, Transformation, Output) graphic shows how the prior-year user list, supervisor approvals, and the new 2026–27 roles become the approval matrix, the current role list, and the access test and review records.
Operational workflow
- Export/review prior users before rollover and obtain current supervisor approvals.
- After July 7, activate coordinator roles first, then assign site and operational roles by need.
- Require current security forms and training before secure work.
- Test access without sharing credentials; resolve site/organization errors.
- Run recurring user reviews and promptly remove access after role changes.
Implementation pathway
Evidence to retain
- Prior-user export
- Approval matrix
- Current role list
- Forms/training proof
- Access tests and periodic reviews
Official guidance and help
- July 2026 CAASPP CommunicationOfficial rollover date and security reminder
- TOMS ResourcesCurrent role instructions
- Test SecurityCurrent forms and controls
Source review completed August 30, 2026. Verify current California requirements, CAASPP and ELPAC manuals, live system status, local policy, pupil records, and final system state before acting.